

Network security for ISPs and enterprises
Our network security service protects your core, edge and management plane with firewall policies, segmentation and access control, so an attack or a mistake doesn’t take your operation down.
10+ years of experience Multi-vendor compatibility Firewall and segmentation Device hardening
Where this service fits in the life of your network
Each service hands a documented network to the next one, so you can start at the stage your network needs today.
- Know what you haveNetwork audit and documentationExplore
- Build what you needNetwork design and implementationExplore
- Make it performNetwork engineering and architectureExplore
- Move it forwardNetwork migration and IPv6Explore
Run an RV park, campground or hotel? NETXIOM applies the same lifecycle to managed guest WiFi.
Security built for operator networks
We review how traffic enters, moves through and leaves your network. Then we apply firewall policies, segmentation and hardening on every device, so an incident stays contained instead of reaching every user.
We work with firewalls and routers from many vendors and adapt each policy to the equipment you already own. When we finish, you get documentation for every rule and the reason it exists.
- Firewall policies at the edge and in the core
- VLAN and VRF segmentation by service type
- Hardening of routers, switches and management systems
- Access control with AAA (RADIUS or TACACS+)
- Anti-spoofing filters and DDoS mitigation
- Separate management network and secure remote access
From review to a hardened network
An orderly process to close gaps without interrupting service.
Review
We review rules, access, exposed services and the configuration of every device to find weak points.
Prioritize
We rank findings by risk and impact, and agree with you on what gets fixed first.
Apply
We implement policies in maintenance windows, with a rollback plan for every change.
Validate
We confirm legitimate traffic flows, blocked traffic stays blocked, and everything is documented.
What a protected network gives you
Smaller attack surface
Only the services your operation needs stay open.
Contained incidents
Segmentation keeps a problem in one segment from spreading.
Controlled access
Every engineer logs in with their own account, permissions and audit trail.
Documented rules
You know what each rule protects and why it exists.
Security applied by network engineers
Our engineers configure security from the point of view of the people who run the network. That way policies protect you without breaking routing, quality of service or your users’ experience.
A rule nobody understands is a rule someone will eventually remove.
Where your network can go from here
Network audit and documentation
Inventory, topology and a findings report, with documentation that holds up for compliance and financing.
Explore network audit and documentation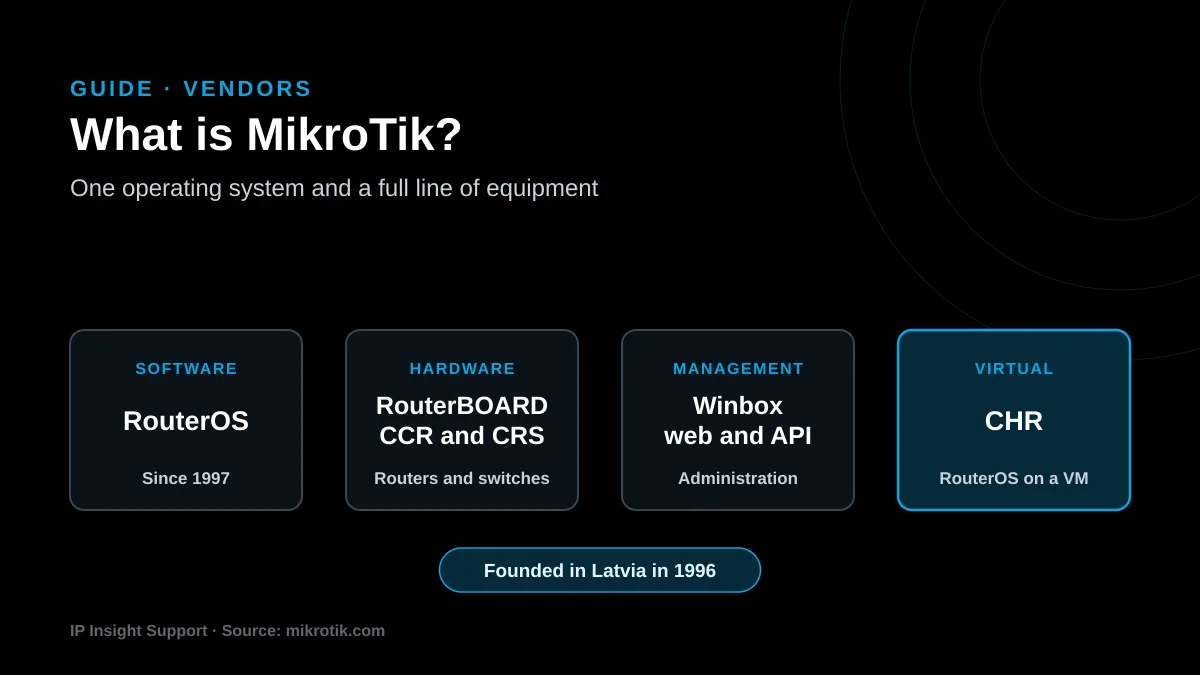
What Is MikroTik? RouterOS and Equipment for ISPs
What MikroTik is and why ISPs, WISPs and businesses use it: routing power, security features and versatility at a cost that scales with the network.
Read the guide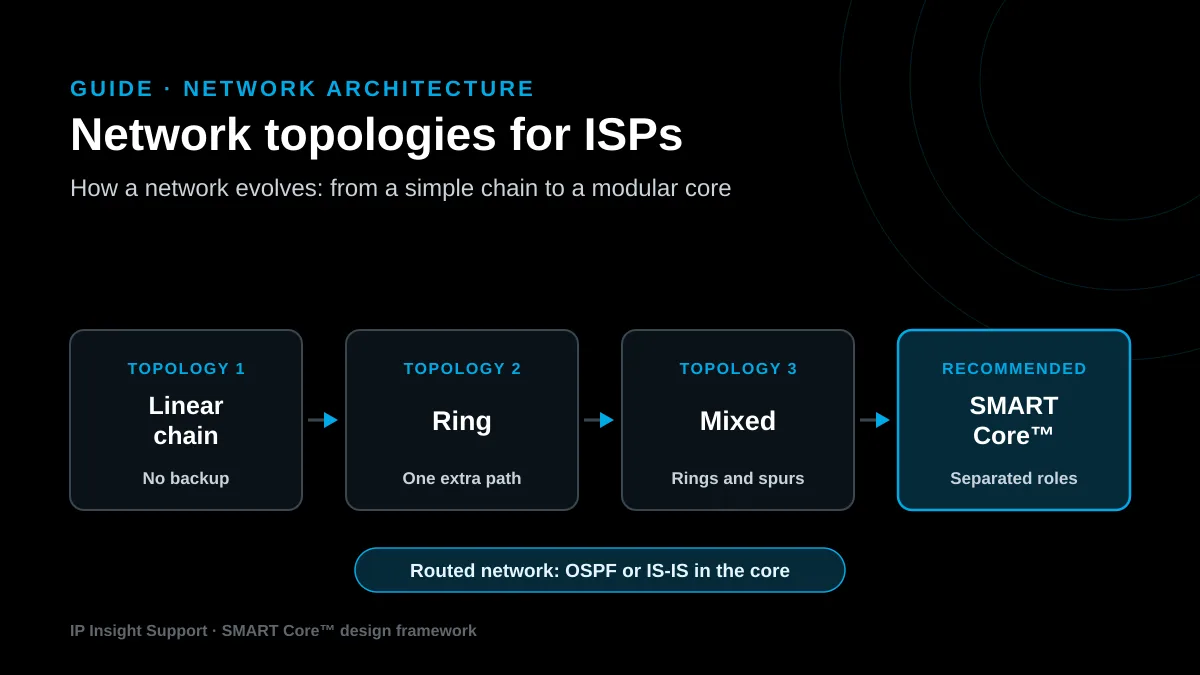
Network Topologies for ISPs: Backbone, Ring and Mixed
How the most common ISP and WISP topologies compare, and how to move past their limits.
Read the guideFrequently asked questions
Do you have another question? Write to us and an engineer will answer, in English or Spanish.
What does the network security service include?
It includes a review of your current configuration, firewall policies at the edge and in the core, VLAN and VRF segmentation, device hardening, AAA access control and a separate management network. At the end you receive documentation for every rule applied.
Do you work with firewalls from different vendors?
Yes. We work with MikroTik, Fortinet, Palo Alto, Juniper and other vendors. We adapt policies to the equipment you already have, without forcing you to switch brands.
Can you help mitigate DDoS attacks?
Yes. We configure filters, rate limits and, when your transit provider offers it, mechanisms such as BGP-signaled blackholing. We also help you define what to do during an attack.
Does security affect network performance?
A well-designed policy shouldn’t degrade service. We validate the processing impact of every rule on your devices before leaving it in production.
What is network device hardening?
It means disabling unused services, closing unnecessary management access, using encrypted protocols and restricting who can manage each device. It reduces the ways into your network.
Do you offer a security audit before making changes?
Yes. If you’d rather know the state of your network first, we start with our network audit and documentation service and set priorities from that report.
Ready to protect your network?
Let’s talk about your current network and define the policies you need to operate with less risk.